🎯 As satellite communications became critical to global connectivity, the cybersecurity bar for frameworks is rising fast. From European directives and frameworks (such as NIS2, the Cyber Resilience Act, and the EU Space Act) to emerging international space security baselines, compliance is no longer just a legal checklist; it is an operational and competitive stake.
🤝 CyberInflight is proud to have developed this newly published White Paper “Impacts of New Cyber Regulations on the SATCOM Ecosystem”, carried out within the European Space Agency – ESA ARTES 4S Cybersecurity Makerspace initiative. Thank you, Hlib Cheporniuk, Patrick Stender, and Stefan Langhammer, for the trust.
🔍 Key takeaways explored in the white paper:
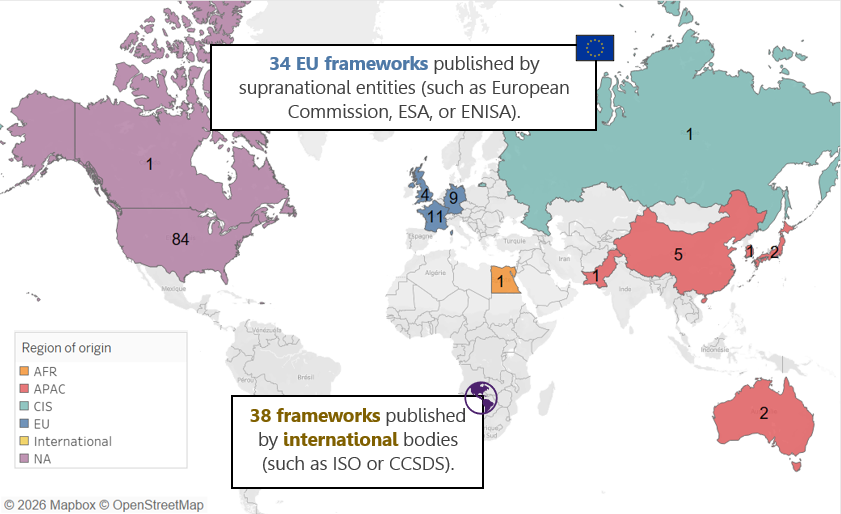
– Landscape overview: A clear mapping of the primary cybersecurity frameworks applicable across the SATCOM and space ecosystems.
– Strengths, gaps, and overlaps: The strengths and ongoing efforts by policymakers, alongside the structural and technical challenges of applying cyber frameworks to space assets.
– Industry realities: How New Space startups, SMEs, and large industrials navigate compliance without compromising agility and operational performance.
– Supply chain impacts: The ripple effects across downstream networks, sub-tier suppliers, and mission lifecycles.
– Policy guidance: Practical, actionable recommendations for regulators to foster adoption and bridge the gap between securization of space systems and the need for operationality and competitiveness of the industry.
👉 Read and download the full White Paper here: 🔗https://urls.fr/-ypxQe
hashtag#SpaceCybersecurity hashtag#SATCOM hashtag#SpaceFrameworks hashtag#CyberCompliance hashtag#SpaceEconomy hashtag#CyberInflight hashtag#ESA hashtag#NewSpace